
In fiscal year 2024, U.S. consumer-product recalls covered about 41 million units, but for the operations lead signing the file, the number that matters is one. One recalled laptop that reaches a resale shelf, or one drive destroyed without a serial record, can undo the work behind thousands of clean returns. Product recall chain of custody services exist to close that gap. They don't just move boxes. They create a linked record of identity, possession, quarantine, sanitization, and final disposition that you can hand to an auditor, regulator, insurer, or internal investigator.
We judge these programs on a simple test. Can you reconstruct what happened to a specific serial number months later, including every exception, or can you only show that a pallet arrived and a certificate was issued?
Table of Contents
- Why Recall Chain of Custody Matters for Compliance
- Selection Criteria for a Recall Custody Provider
- Matching Data Destruction Methods to Each Device
- Custody Events and Workflow From Pickup to Certificate
- Securing Transport, Staging and Exception Handling
- Implementation Checklist and Sample Custody Form
- Confirm Custody Coverage Before Your Next Recall
Why Recall Chain of Custody Matters for Compliance
One missed unit is the starting point. A recall population is defined by serial number, lot, model, component, or firmware version, not by age or condition. If that unit isn't captured, it can remain deployed, get resold, or enter a secondary channel with data still readable. A count that looks close enough doesn't answer the only question that creates liability. Where is that specific device now?
Scale explains why manual control breaks quickly. The U.S. Consumer Product Safety Commission negotiated 333 voluntary recalls involving approximately 41 million units in fiscal year 2024 and issued 2,969 notices of regulatory violations, according to the CPSC fiscal year 2024 annual report. Of those voluntary recalls, 166 used the Fast-Track program, and 98.08% of Fast-Track recalls started within 20 days after a company reported the problem. Deadlines measured in weeks leave no time to design tracking after the announcement.
What the Service Actually Does
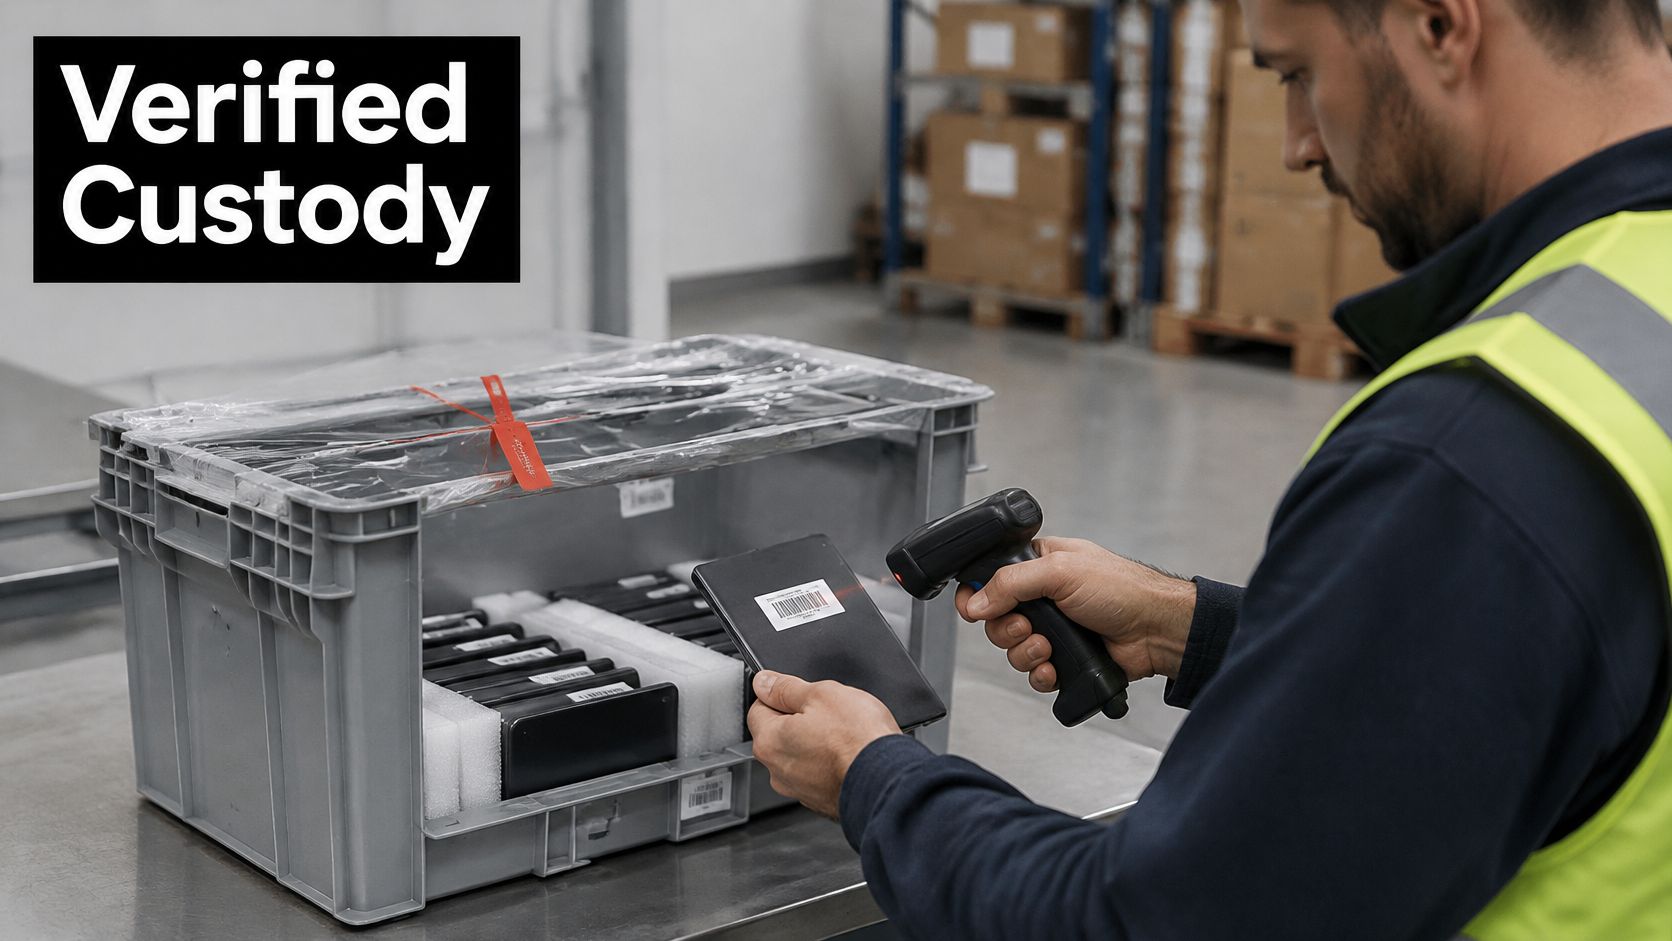
A custody provider takes physical possession of affected units, logs each handoff against a unique identifier, holds them separately from normal inventory, applies the required sanitization, destruction, return, or recycling action, and returns evidence you can file. Think of a sealed evidence bag passed between officers. Each person signs the tag, so nobody can later claim the item was never received or was handled by someone else.
That's different from routine IT disposal. In a refresh, you choose which assets leave because they're old, broken, or surplus. In a recall, the affected population is imposed on you, and completeness matters more than speed alone. You need to prove that identified units were isolated and dispositioned, not merely collected.
A custody log proves a unit was removed from circulation. It doesn't, by itself, prove the underlying risk was reduced.
Two failure modes drive the design. First, an unaccounted recalled unit re-enters commerce. Second, residual data remains exposed after a product is crushed, recycled, or transferred. A defensible provider controls both at once through serialized identity, segregated storage, documented transport, verified sanitization or destruction, and a certificate tied to the actual serial list.
Before you go further, test your current process with one serial number. Ask for its pickup record, receiving scan, staging location, disposition decision, verification result, and final certificate. If any link depends on memory or a spreadsheet edited after the fact, the chain won't survive a serious audit.
Selection Criteria for a Recall Custody Provider
Vendor selection starts with due diligence, not price. For organizations covered by the FTC Disposal Rule, due diligence can include reviewing a destruction provider's independent audit, checking references, confirming recognized trade-association certification, and evaluating information-security policies, as described in the FTC guidance on disposing of consumer report information. The rule also identifies destroying or erasing electronic media so information can't be read or reconstructed as an example of compliant disposal.
Request the evidence before you request pricing. A provider that can't produce samples during evaluation won't produce better records under recall pressure.
Provider Qualification Criteria for Recall Custody
| Criterion | What to request | Red flag |
|---|---|---|
| Independent audit | Current third-party audit report of data and custody controls | Audit older than 12 months or none offered |
| Trade-association certification | Certificate numbers for recognized recycling or data-destruction programs | Claims without a verifiable certificate number |
| Serialized receiving | Sample scan export showing asset-level intake | Count-only receiving or manual logs |
| Certificates per batch | Sample certificate listing serials, method and date | Generic certificate with no serial list |
| Transport controls | Sealed or locked vehicles, GPS tracking and signed manifests | Subcontractor with no chain documentation |
| Liability and insurance | Coverage limits for handling and data incidents with certificate of insurance on request | No stated limits or no certificate offered |
| Enterprise references | Three recent references from comparable buyers | Anonymous or unverifiable references only |
Use the table as a pass or fail screen. Vague language on serial-level receiving should end a recall evaluation. Count-only receiving can prove that boxes arrived, but it can't prove which affected units were removed or whether a non-recalled unit filled the count.
The same logic applies when you're reviewing the broader questions to ask before hiring an ITAD company. For recall work, add contract terms that name the required controls directly.
- Named custody events: Define each required scan, handoff, and approval in the agreement.
- Certificate turnaround: Set a deadline and require the full serial list, method, and date.
- Liability and insurance: Record coverage limits and incident-notification duties.
- Subcontractor disclosure: Require written notice before another party transports or processes units.
- Record retention: State how long scan exports, photos, reports, and certificates remain available.
One factual example in this market is Beyond Surplus, an Atlanta-based ITAD and electronics recycler that issues certificates of recycling and data destruction, offers on-site or off-site hard drive shredding and certified wiping, and schedules business pickups across the contiguous United States using its own fleet and transport partners. Evaluate any provider the same way, against documents rather than sales language.
Apply a simple ranking rule. A provider that meets every criterion beats a cheaper provider with a missing audit, generic certificate, or count-only intake. The price difference is small compared with the cost of rebuilding a recall file after disposition is complete.
Matching Data Destruction Methods to Each Device
NIST separates media sanitization into Clear, Purge, and Destroy. Clear uses logical techniques while generally preserving reuse. Purge uses physical or logical techniques intended to make recovery infeasible even with state-of-the-art laboratory methods. Destroy makes recovery infeasible and prevents the media from being reused for data storage. Those definitions come from NIST Special Publication 800-88 Revision 1, which frames sanitization as making access to target data infeasible for a specified level of effort.
Don't select the method from the device label alone. Categorize the information, assess the medium, evaluate confidentiality risk, and decide the asset's future disposition. A functioning drive that stays inside your controlled chain may justify Purge and reuse. A drive leaving your control, failing verification, or carrying higher-risk data may require Destroy.
Sanitization Method by Device Type
| Device | Typical method | Verification | Certificate fields |
|---|---|---|---|
| Laptop or desktop hard drive (HDD) | Purge by overwrite or ATA secure erase when reuse is planned; Destroy if the drive is unreadable | Per-unit verification | Manufacturer, model, serial, media type, method, technique |
| Laptop or desktop solid-state drive (SSD) | Purge by cryptographic erase or ATA secure erase; overwrite alone is unreliable | Per-unit verification | Manufacturer, model, serial, media type, method, technique |
| Data center server drives | Purge where the drive stays in the owner's chain; Destroy where it leaves that control | Per-unit verification | Property number, serial, drive count, method, destruction record |
| Failed or unreadable drives | Destroy by shredding; degaussing does not apply to SSDs | Destruction record with weight or count | Serial, destruction method, facility, date |
| Smartphones and tablets | Purge using vendor-supported wipe; Destroy if the wipe fails | Per-unit verification where the platform allows it | Manufacturer, model, serial or IMEI, media type, method, technique |
| Medical or laboratory equipment with embedded storage | Hold for records-retention review, then Purge or Destroy | Per-unit verification plus retention sign-off | Device ID, storage component, retention decision, method |
Two drives can look identical and require different outcomes. A readable laptop drive approved for resale should be purged and verified per unit, with the result tied to its serial number. A drive from a failed array that won't report a readable state can't produce the same proof, so destruction is the defensible choice. Forcing both through one workflow creates either unnecessary loss or unsupported assurance.
Embedded storage adds another decision. Medical devices, laboratory equipment, controllers, and diagnostic systems may hold records that can't be destroyed until retention obligations are reviewed. Hold those units in quarantine, get the retention decision in writing, and record which storage component was sanitized. The device serial alone may not identify the internal drive, card, or module that carried the data.
For a fuller explanation of the decision framework, review the NIST 800-88 data destruction standards guide before you lock a recall procedure. Then choose verification deliberately. Verify every unit when confidentiality risk is high, when media will leave your control, or when regulators may test individual records. Use representative sampling only when policy permits it, the sample is documented, and failures trigger a defined expansion or destruction rule.
Verification rule: A completed wipe message isn't evidence unless it's linked to the serial number, tool, method, date, and person or system that verified the result.
Custody Events and Workflow From Pickup to Certificate
Every custody record must link to a unique serial, lot, shipment, or destruction batch identifier. Without that link, scans become warehouse activity rather than evidence. The table below is the minimum event model we expect a provider to fill for a recall batch.
Custody Events and Required Records for a Product Recall
| Custody event | Responsible party | Required record | Evidence kept |
|---|---|---|---|
| Recall authorization | Client compliance lead | Recall reference, affected models, serial or lot ranges, authorization date | Signed authorization letter |
| Pickup | Carrier driver and client site contact | Pickup timestamp, site address, manifest, seal number | Signed manifest and seal photo |
| Receiving | Provider receiving technician | Scanned serial numbers, counted quantity, variance log | Scan export reconciled to manifest |
| Quarantine and staging | Provider inventory lead | Storage location ID, segregation status, access entries | Access log and location record |
| Sanitization or destruction | Certified technician or facility operator | Method (Clear, Purge or Destroy), tool used, verification result | Verification report and process photos |
| Final disposition | Provider recycling or destruction facility | Destruction or recycling date, facility ID, material outcome | Weight or destruction ticket |
| Closeout | Provider compliance manager | Certificate number, full serial list, client signature | Signed certificate of recycling or destruction |
For electronics with storage media, the certificate needs asset-level detail. NIST SP 800-88r2 recommends a certificate for each sanitized item identifying manufacturer, model, serial number or property number, media type, sanitization method, and technique, as set out in NIST SP 800-88r2. The identity fields establish what the item was, the custody log establishes who possessed it, and the certificate proves the final risk-reduction action.
Scan at pickup, receipt, quarantine, processing, and final disposition. Reconcile each scan set against the manifest, segregate recalled assets from resale inventory, and record damaged or unreadable labels as exceptions. Don't let technicians repair identity problems informally by typing a likely serial number into a spreadsheet. Preserve the original scan, note the inspection, and attach the resolution.
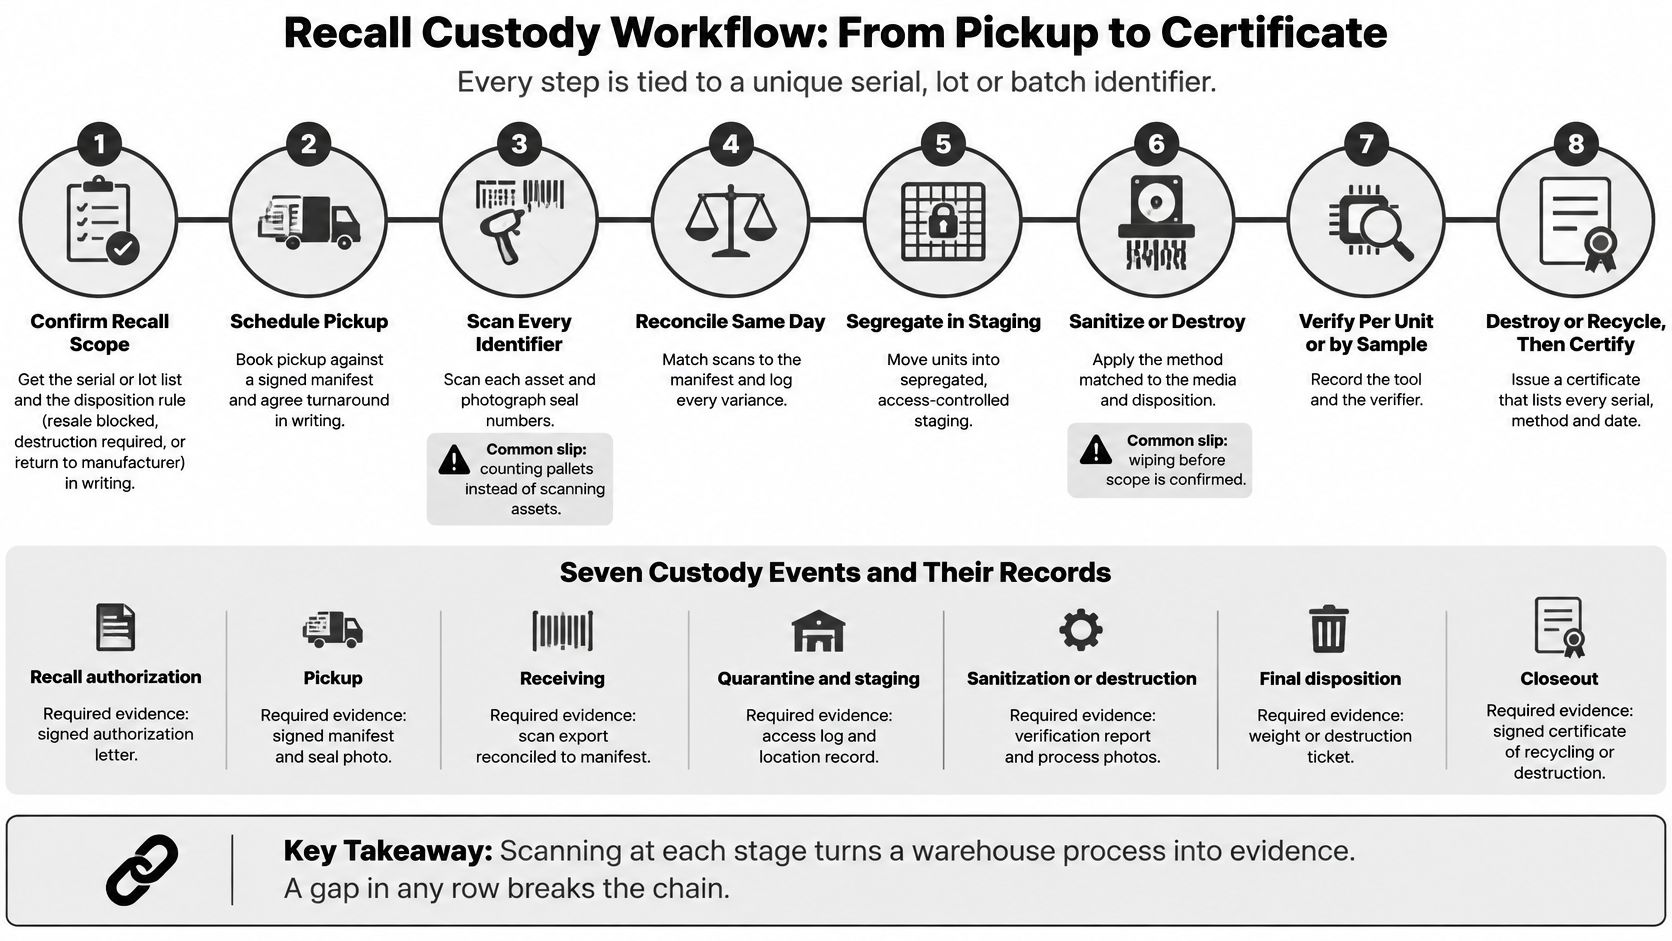
Eight Steps From Scope to Closeout
Confirm recall scope in writing. Record the serial or lot list and the disposition rule for every population. State whether resale is blocked, destruction is required, return to manufacturer is required, or remediation is allowed. This prevents the most damaging early error, processing units before anyone agrees what outcome is authorized.
Schedule pickup against a signed manifest. Agree the site contact, pickup window, packaging method, expected count, and turnaround before the truck is dispatched. A manifest created after loading isn't a control. It's a summary.
Scan every identifier and photograph seal numbers. Scan assets, not pallets, and capture container or trailer seals before departure. The common slip is counting cartons and discovering at receiving that the count is right but the identities are wrong.
Reconcile scans against the manifest the same day. Compare expected serials, scanned serials, quantity, model, and site. Log every variance while the driver, site contact, and receiving technician can still resolve it from source records. Waiting until closeout turns a correctable mismatch into an unexplained gap.
Move units into segregated, access-controlled staging. Assign a storage location ID and a visible recall status. Keep recalled units physically separate from resale, repair, redeployment, and general recycling stock. Segregation fails when it exists only as a status code in a system that warehouse staff can't see.
Sanitize or destroy using the approved method. Match Clear, Purge, or Destroy to the media, data risk, and disposition rule. Don't wipe before scope is confirmed, and don't substitute a faster method because equipment is unavailable. Record any approved change before processing continues.
Verify and record who verified. Verify per unit or through a documented representative sample allowed by policy. Capture the tool, result, verifier, and failure path. Failed units should move to a defined hold or destruction queue, not back into the general batch.
Complete final disposition and issue the certificate. Destroy, recycle, return, or remediate according to the written rule. Issue a certificate listing every serial, method, facility, and date, then reconcile the certificate list to receiving and exception records before the client signs closeout.
Here, the data model matters more than scan volume. A provider can generate thousands of scans and still fail if serial, lot, component, firmware, location, and disposition records don't join cleanly. Ask how the system handles a duplicate serial, a missing label, a unit from the wrong site, and a replacement device containing the same affected component. The answers reveal whether exception handling was designed or improvised.
A structured product recall reverse logistics service should make those joins visible during the project, not only in a final PDF. You should be able to see received count, quarantined count, processed count, failed verification count, destroyed count, and unresolved exceptions by batch or site.
Scanning at each stage turns a warehouse process into evidence. A gap in any custody row breaks the chain, even if every other row is perfect.
Before signing, ask the provider one direct question. Which row in the custody table can't you complete with system-generated evidence? A candid limitation can be managed in the contract. A vague assurance usually becomes a missing record when legal, compliance, or a regulator asks for the file.
Securing Transport, Staging and Exception Handling
A single unaccounted unit matters more than a reassuring completion percentage. If that unit is resold, redeployed, or discarded with readable data, it creates the exposure the recall was meant to remove. Transport and staging controls should therefore protect identity as well as physical possession.
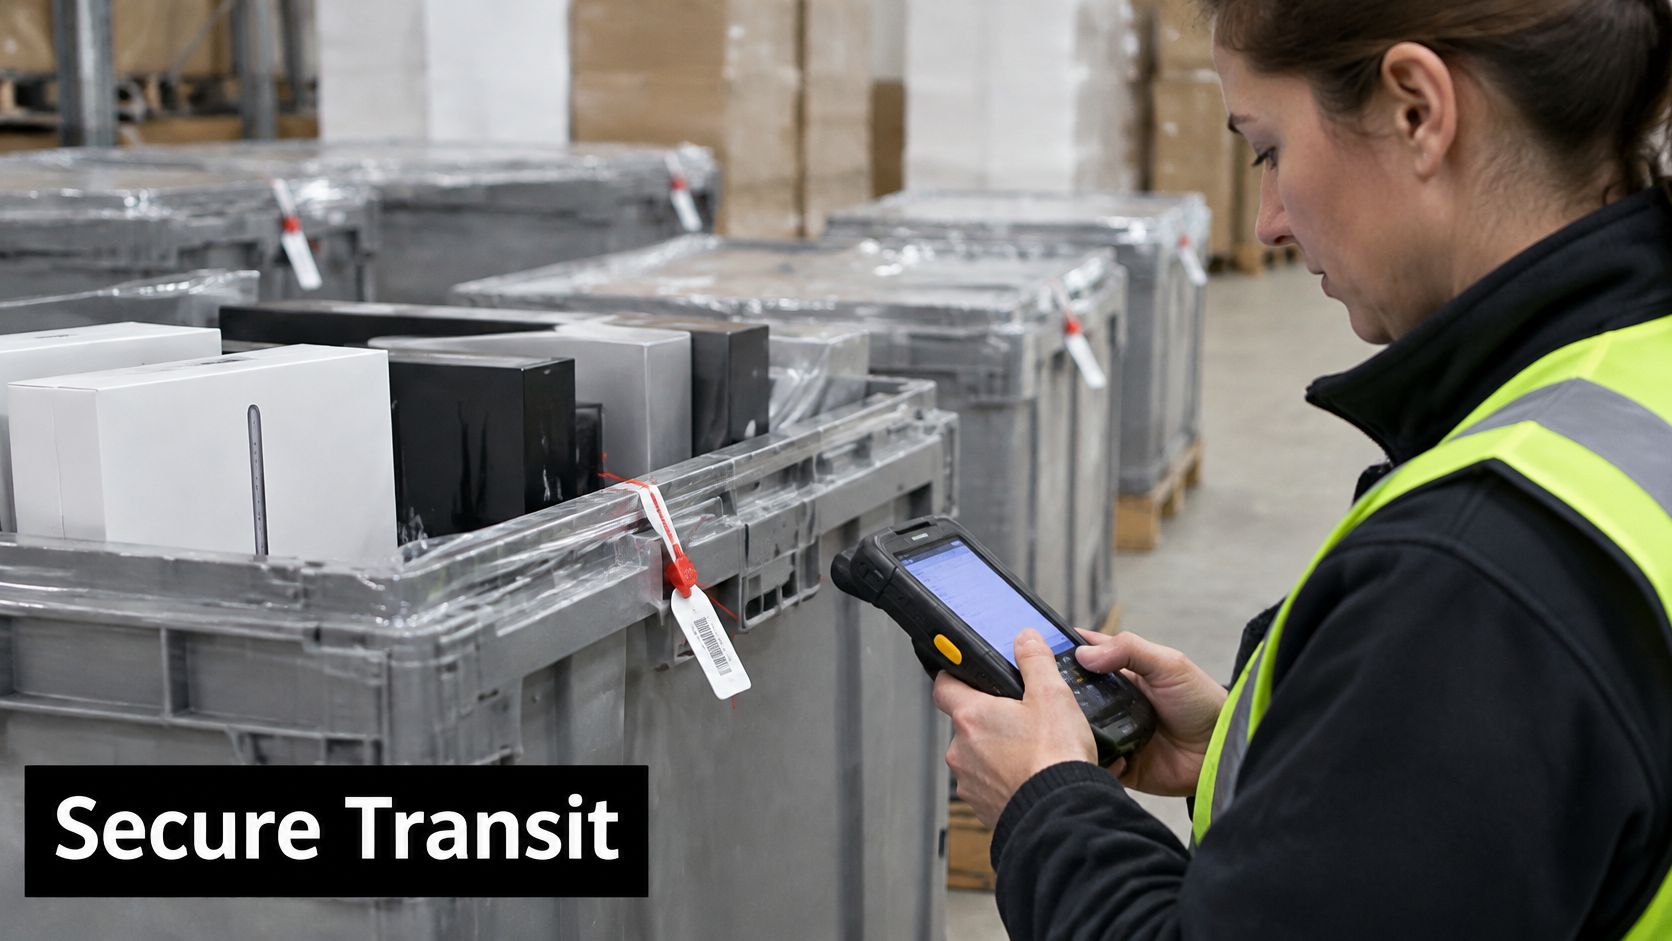
Controls During Movement and Storage
- Sealed containers or locked trailers: Record seal numbers at pickup and verify them at receiving before unloading.
- GPS-tracked vehicles: Tie the vehicle or shipment identifier to the manifest and pickup timestamp.
- Two-person handling: Use it for high-value servers, controllers, and batches where diversion risk justifies added oversight.
- Disclosed subcontractors: Prohibit transfer to another carrier or processor without written disclosure and matching custody records.
- Access-controlled staging: Maintain entry logs, named storage locations, and segregation labels visible on the physical units.
- Status separation: Keep recalled stock away from resale, repair, warranty, and redeployment inventory at all times.
Exceptions shouldn't be treated as clerical noise. Each one needs a rule, an owner, a deadline, and a written outcome.
Exception Rules That Prevent Quiet Failures
Missing or unreadable serial number. Stop the unit, inspect it physically, photograph identifying marks, and document the basis for any assigned identifier. Don't guess.
Count mismatch. Escalate the same business day to the site contact and provider operations lead. Keep the batch open until the variance is explained or formally accepted.
Broken or mismatched seal. Place the shipment on hold, notify the client, inspect contents against the manifest, and record who authorized further handling.
Unit not on the manifest. Quarantine and report it. Don't add it without documentation, because it may belong to another recall population, site, or disposition rule.
Recalled unit found in a resale channel. Issue an incident report, preserve listing or transaction evidence, identify the last documented custodian, and review every batch handled through the same path.
Close the loop with a named escalation path. The receiving lead notifies the provider compliance manager, who notifies the client recall lead in writing with the affected identifiers, evidence, containment action, and next decision required. Phone updates can happen, but they don't replace the record.
Implementation Checklist and Sample Custody Form
Don't test your custody form during the first live pickup. Build it from the records you'll need during an investigation, then confirm every field has an owner and a source system. Fields that rely on free-text memory will be completed inconsistently under volume.
Pre-Pickup and Closeout Checklist
- Scope approved: Recall reference, affected identifiers, and disposition rule are signed.
- Inventory reconciled: Serial or lot list matches the asset inventory and site locations.
- Retention cleared: Privacy, legal, and records owners approve destruction timing where required.
- Method assigned: Media type, sanitization action, verification level, and failure path are defined.
- Exceptions owned: Escalation contacts and response deadlines are named before pickup.
- Certificate reviewed: Final serial list reconciles to receiving, processing, and exception records.
- File retained: Complete custody package is stored for the period set by company policy.
The checklist intentionally focuses on decisions and approvals around the workflow. The operational scans still matter, but a scan can't cure an undefined disposition rule or an unresolved retention hold.
Sample Custody Form Fields
| Form area | Fields to capture |
|---|---|
| Recall identification | Recall reference, client site, site contact, affected model, serial or lot range |
| Pickup | Pickup date and time, carrier, vehicle or shipment ID, seal numbers, driver signature |
| Quantity control | Expected count, scanned count, variance, explanation, escalation owner |
| Asset identity | Asset identifier list, manufacturer, model, property number, media type |
| Staging | Receiving timestamp, storage location ID, segregation status, access entries |
| Processing | Sanitization method, technique, tool, verifier name, verification result |
| Final disposition | Destruction or recycling facility, facility ID, date, material outcome |
| Closeout | Certificate number, full serial list, client signature, provider signature |
Use the same form structure for internal investigations. If a unit is questioned later, investigators should be able to move from recall authorization to pickup, receipt, staging, processing, and disposition without asking the warehouse team to reconstruct events from email.
Currency matters in the procedure itself. NIST SP 800-88 Revision 1 was withdrawn on September 26, 2025, when it was superseded by Revision 2, according to the NIST publication record for SP 800-88 Revision 1. Update policies, contract language, and provider procedures so they cite the current publication rather than treating Revision 1 as the latest guidance.
That review should happen before destruction. Consult privacy officials, records-retention personnel, and other required reviewers where media is embedded in servers, diagnostic devices, controllers, or medical and laboratory equipment. Retention obligations can change both timing and method.
A usable audit trail reporting process should export these fields without manual reassembly. Ask for a sample export using test serials and check whether timestamps, responsible parties, exceptions, and certificate numbers remain linked after export. If the provider can only send screenshots, your audit workload will grow with every batch.
Confirm Custody Coverage Before Your Next Recall
Make the decision in four actions.
First, map the recall scope. Convert the affected population into serial and lot ranges, sites, quantities, and disposition outcomes. Separate units for destruction, manufacturer return, repair, replacement, or restricted reuse. If a component or firmware version defines the risk, record that attribute as well. A finished-product serial list alone may not identify every affected configuration.
Second, score the provider against documented criteria. Confirm the independent audit, certifications, serialized receiving sample, transport controls, insurance, references, and sample certificate. Reject generic paperwork that can't be tied to individual units.
Third, put custody events in the contract. Name the authorization, manifest, seal, scan, quarantine, verification, disposition, exception, and closeout records required for each batch. Include turnaround, record retention, subcontractor disclosure, incident notification, and who can authorize a method change.
Fourth, run a pilot pickup. Use a small batch with normal units and at least one controlled exception, such as a missing manifest line or unreadable label. The pilot shows whether receiving reconciles the same day, whether staff quarantine instead of improvising, and whether certificates arrive complete and on time. Don't let a full recall be the first test.
Review the full scope of secure and sustainable product destruction services when destruction, rather than return or remediation, is the required outcome. Then request a scoped quote based on identifiers, locations, media types, verification level, and evidence requirements. A quote based only on pallet count won't tell you whether custody coverage is real.
Contact Beyond Surplus for certified electronics recycling and secure IT asset disposal.
For recalled electronics that require serialized pickup, quarantine, verified data destruction, product destruction, and certificates tied to the final serial list, contact Beyond Surplus to scope the custody records and disposition evidence before the first truck is scheduled.


