
A refresh project just finished, and the retired equipment is sitting in a warehouse, data center aisle, or locked office. Finance sees depreciated assets. IT sees cleanup. Auditors see a chain-of-custody question. The right approach to selling used enterprise IT equipment treats remarketing as a timing-and-proof decision, not a simple depreciation exercise.
Table of Contents
- Why Most Enterprises Leave Money and Compliance on the Table
- Choosing Between On-Site and Off-Site Data Sanitization
- Meeting the FTC Disposal Rule and Adjacent Compliance Demands
- Comparing ITAD Buyback, Brokers, Auctions, and Direct Remarketers
- Planning De-Installation, Logistics, and Chain of Custody
- Pricing for Maximum Recovery in an AI-Driven Secondary Market
- Contracts, Transfer of Liability, and Post-Sale Reporting
Why Most Enterprises Leave Money and Compliance on the Table
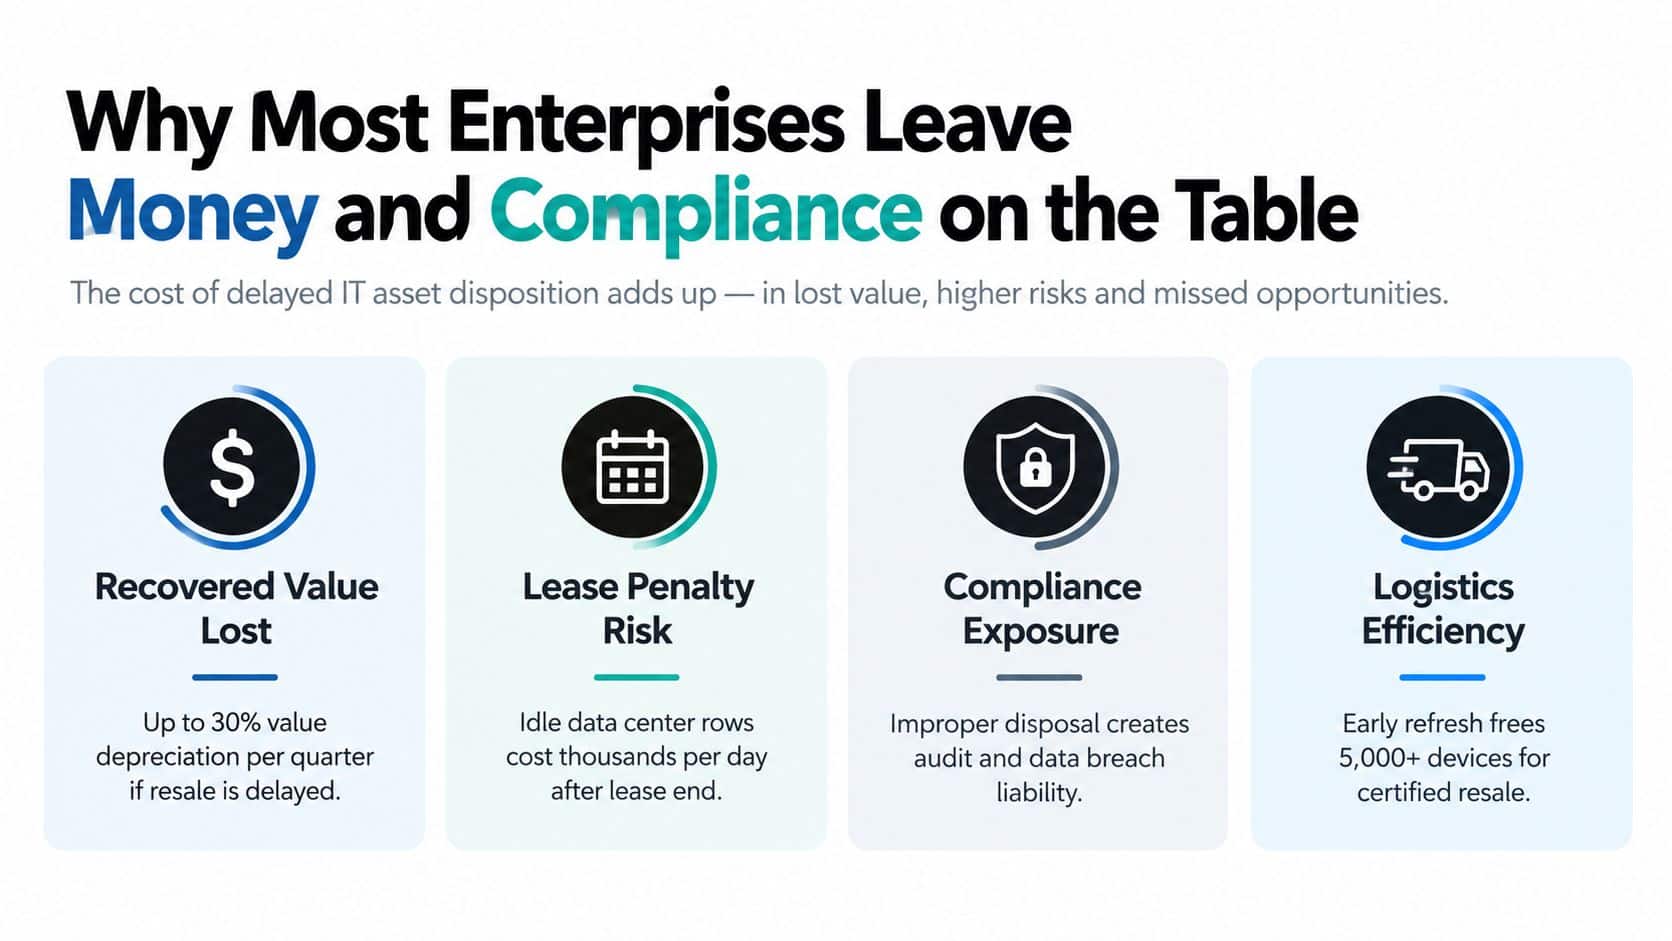
A 5,000-seat laptop refresh can finish ahead of schedule, leaving thousands of working devices ready for disposition while the replacement project is still active. A data center decommission can free an entire row before a lease ends. In both situations, the important question isn't only whether the equipment can be sold. It's when to release it, how to value it, and what evidence the buyer and auditor will require.
Enterprise servers can retain about 35–45% of original value at two years, 25–35% at three years, and 15–25% at four years, assuming remarketing occurs within six months of retirement. At five years or older, recovery commonly falls to single digits. Remarketing can also offset roughly 40–60% of total disposition costs compared with recycling-only programs, according to the 2026 ITAD value-recovery guide.
Build one defensible inventory
Start with a single inventory assembled from the CMDB, procurement records, and finance data. Reconcile it against a physical audit that records:
- Identity: Manufacturer, model, serial number, and asset tag.
- Configuration: Processor, memory, storage, GPU, networking cards, rails, and accessories.
- Condition: Operational status, cosmetic wear, missing components, and packaging.
- Disposition path: Remarketing, recycling, parts recovery, or destruction.
Use a consistent grading rubric. Grade A covers like-new operational equipment with original packaging. Grade B means working equipment with light wear. Grade C identifies functional units with visible cosmetic impairment. Grade D is parts-only or end-of-life material.
Value the inventory against current secondary-market comparisons and lot-level demand, not book value. A practical recovery-rate calculation is dollars recovered divided by original acquisition cost, compared by asset class each quarter. That gives leadership a metric it can defend and reveals which models deserve remarketing rather than destruction. The enterprise asset retirement guide provides a useful reference for structuring that baseline.
Practical rule: Don't move equipment into a sales channel until inventory, condition, data status, and expected recovery are tied to the same serial-level record.
Choosing Between On-Site and Off-Site Data Sanitization
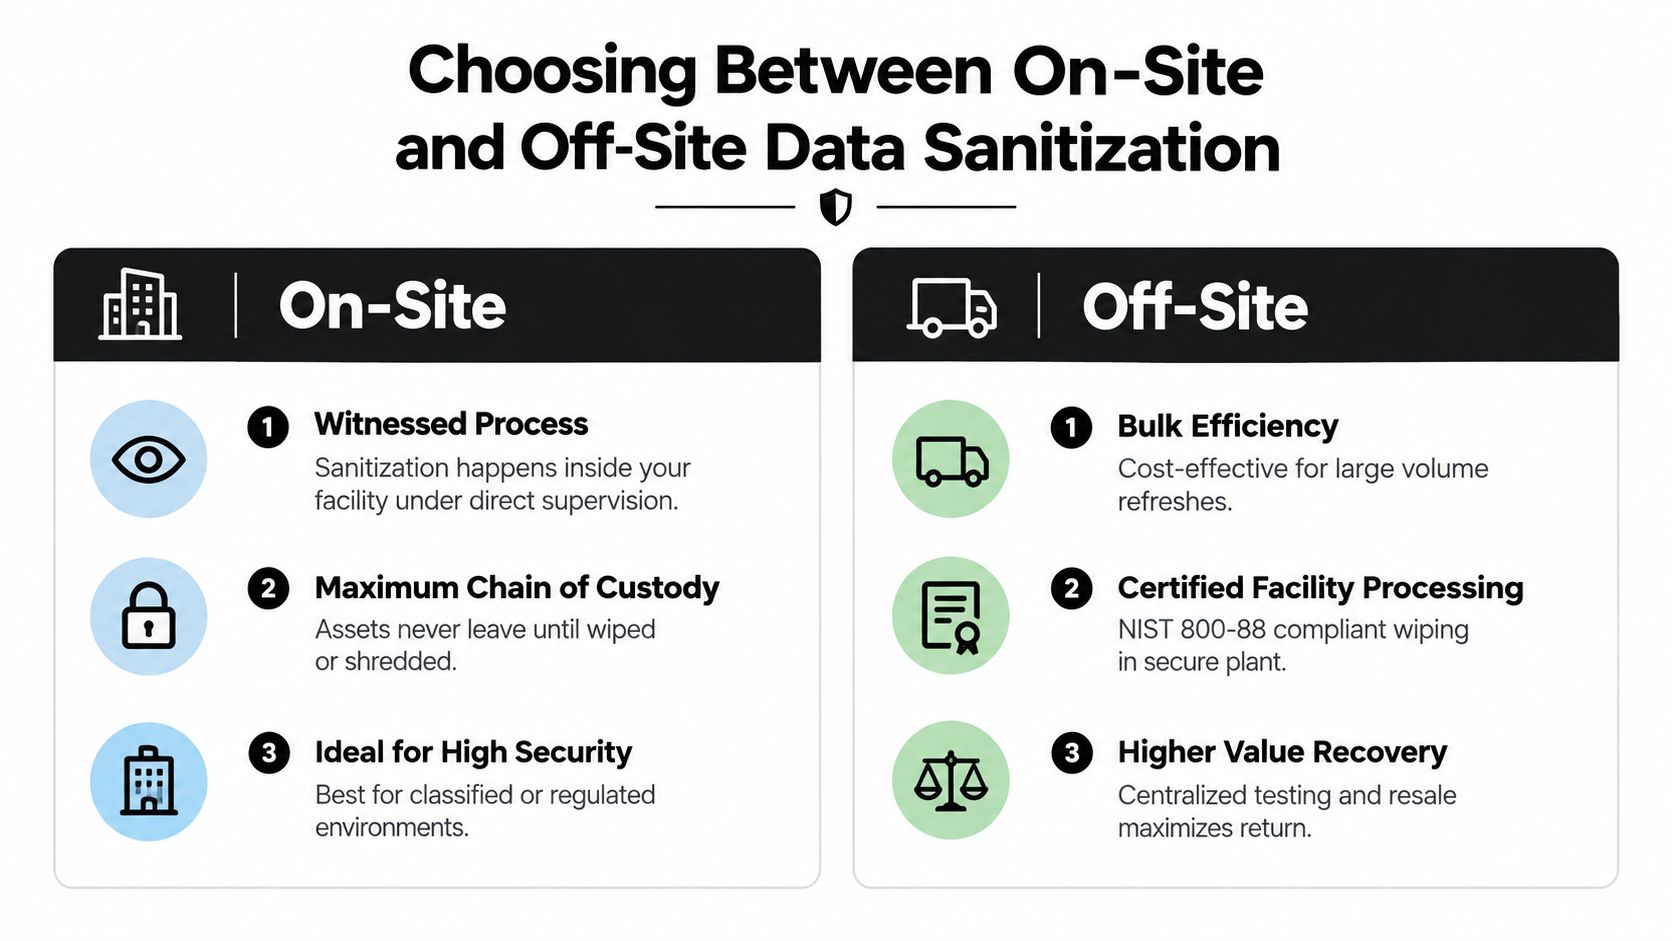
Sanitization should follow the data classification and audit risk, not habit. On-site wiping or shredding keeps equipment inside the facility, allows staff to witness the work, and reduces concern about transport before data removal. It's the stronger choice for classified workloads, regulated environments, and buyers that require direct observation.
The trade-off is operational. On-site processing costs more per drive and uses facility space and staff time. Physical destruction also eliminates resale potential for the affected media, so it should be reserved for drives that cannot be reliably sanitized or that fall under a destruction requirement.
Off-site processing can improve throughput
An accredited off-site ITAD facility can process large refreshes more efficiently and centralize testing, grading, and resale preparation. That option is acceptable only when the provider supplies serialized sanitization certificates, tamper-evident chain-of-custody records, and auditable facility controls. Procurement should verify applicable R2v3 or NAID AAA credentials instead of accepting a generic “secure facility” statement.
Use on-site service when transport is itself a compliance concern. Use off-site service when the vendor's controls are documented, the asset volume is substantial, and faster processing improves recovery timing. The on-site versus off-site ITAD comparison helps teams evaluate that decision without treating either method as universally superior.
Meeting the FTC Disposal Rule and Adjacent Compliance Demands
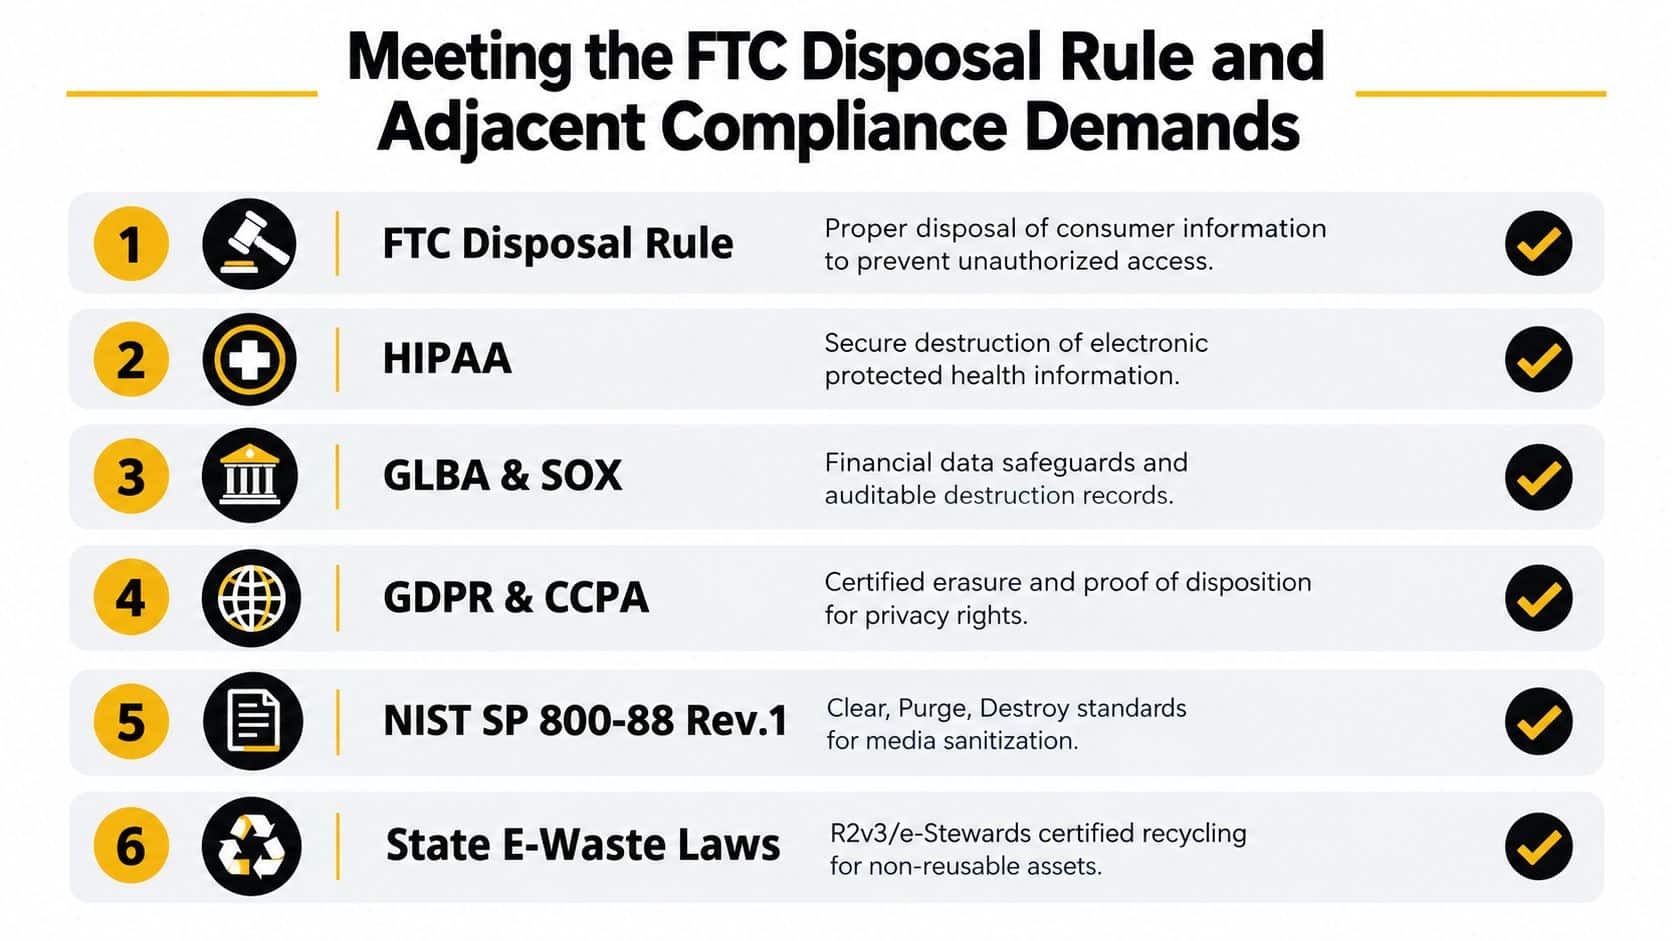
The FTC Disposal Rule applies to any business or individual that uses consumer reports for a business purpose. It requires disposal methods that are reasonable and appropriate to prevent unauthorized access to consumer-report information, as explained in the FTC's disposal guidance.
That rule is the floor, not the complete enterprise control framework. Healthcare, finance, education, and government organizations often face contractual, privacy, security, and insurance requirements that demand stronger evidence than a basic disposal statement.
Documentation auditors can follow
A defensible program should identify who approved disposition, which method applied to each device, who handled the asset, and when custody changed. Require:
- A written sanitization plan: Define clear, purge, and destroy decisions by media type and data classification.
- Serialized records: Tie every drive, laptop, server, and storage component to an asset record.
- Certificates: Obtain certificates of data destruction or media sanitization for each applicable asset.
- Chain-of-custody logs: Record pickup, transport, receiving, processing, and final disposition.
- Retention rules: Keep records according to the organization's legal, contractual, and security requirements.
NIST SP 800-88 Rev. 1 can provide the technical reference for media sanitization, while HIPAA, GLBA, SOX, GDPR, CCPA, and state electronics laws may create additional obligations. Buyers, cyber insurers, and SOC 2 auditors may also request third-party attestations, certified recycling controls, overwrite or purge verification, and witnessed destruction for sensitive workloads.
The corporate electronics disposal guide can help procurement and security teams organize the questions they should put to legal, IT, and their ITAD provider.
Comparing ITAD Buyback, Brokers, Auctions, and Direct Remarketers
The sales channel determines more than price. It also determines who controls the buyer relationship, who carries downstream risk, how quickly equipment leaves the building, and how much evidence leadership receives after settlement.
Sales Channels Compared for Enterprise IT Resale
| Channel | Recovery Potential | Liability Transfer | Compliance & ESG | Cycle Time | Reporting Depth |
|---|---|---|---|---|---|
| ITAD buyback | Predictable and efficient | Concentrated with one provider | Depends on provider controls | Fast | Usually strong |
| Brokers | Competitive reach | Must be defined contractually | Varies by downstream buyer | Moderate | Can be uneven |
| Auctions | Potentially strong gross recovery for commodity gear | Often limited unless written into terms | Buyer screening is critical | Variable | Depends on platform |
| Direct remarketers | Greater control over brand and disposition | Negotiated directly | Often easier to align with sustainability goals | Slower for niche inventory | Can be detailed |
An ITAD buyback works well when speed, predictable settlement, and removal capacity matter more than maximum upside. It's often the right choice for mixed laptop lots, older networking equipment, and projects with lease or storage pressure.
Brokers can expand buyer reach, but their markup, process length, and downstream visibility require scrutiny. Auctions may generate strong interest in standardized commodity hardware, yet an unknown buyer can create reputational, data-handling, and ESG exposure. Direct remarketers and OEM trade-in programs offer tighter control, but they may provide less price discovery.
Score every channel against recovery transparency, liability transfer, compliance posture, cycle time, ESG controls, and reporting depth. For enterprise rack servers and networking gear, a structured data center equipment buyback process is usually preferable to a blind bulk sale.
Planning De-Installation, Logistics, and Chain of Custody
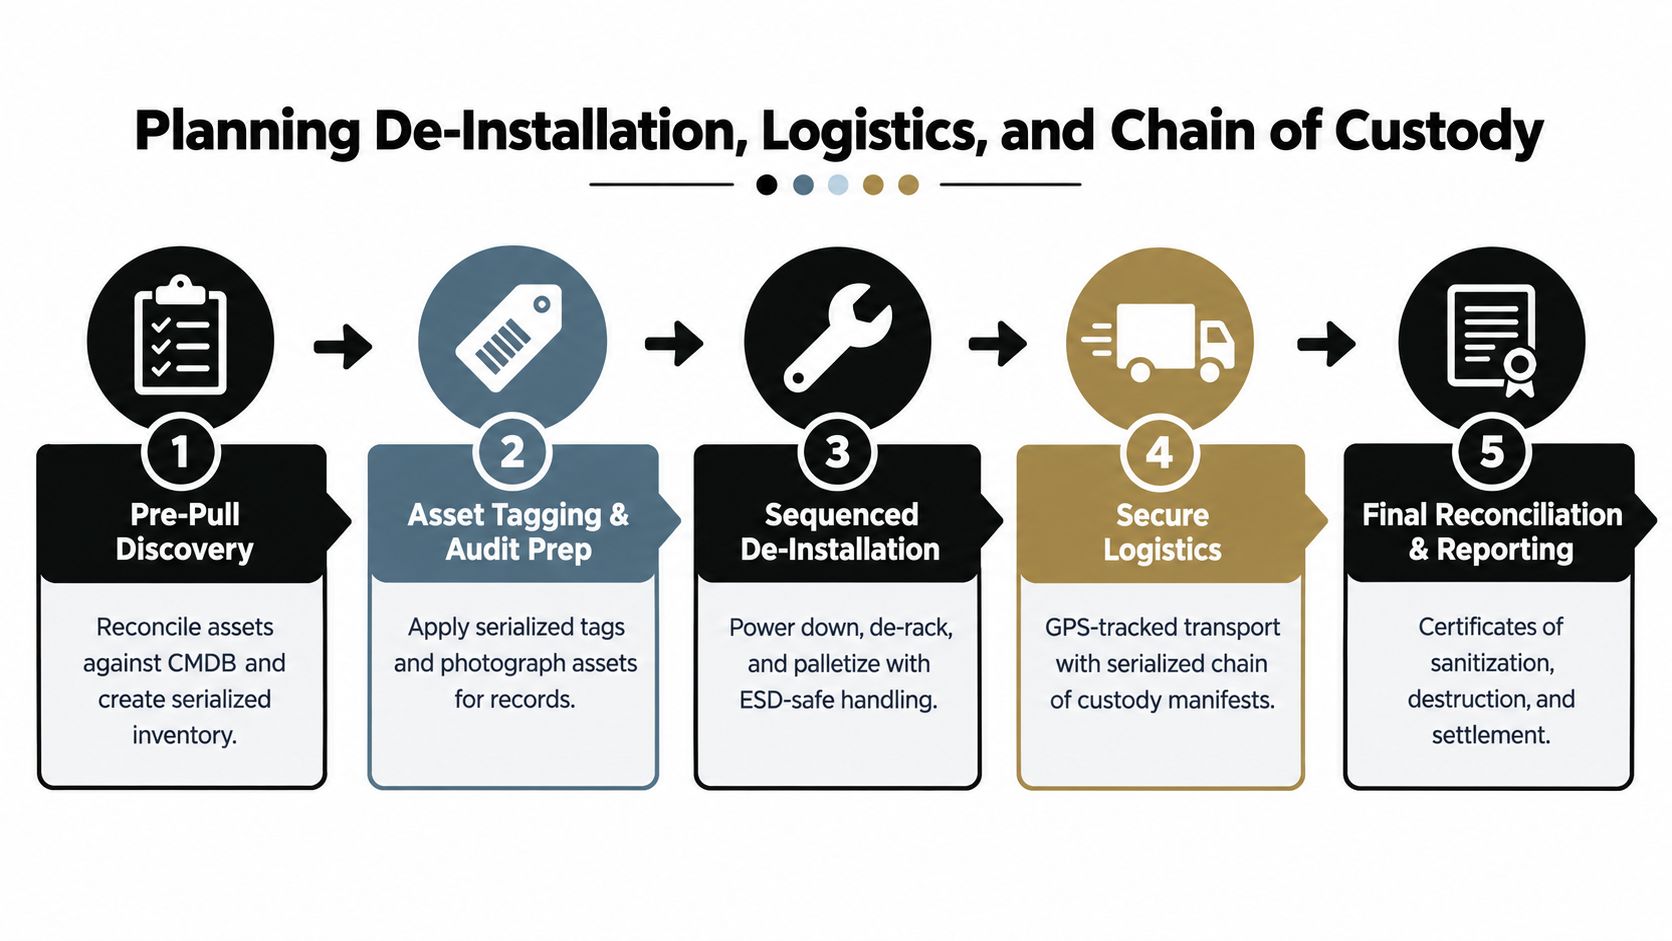
A sale can lose value before the truck arrives if de-installation is treated as general labor. Build a pre-pull plan that reconciles the CMDB, identifies each serialized asset, captures condition photos, and assigns every unit to sanitize, destroy, recycle, or remarket before removal. That decision determines both recovery potential and the proof an auditor can review.
Control the pull and handoffs
Use a manifest-driven pull rather than a generic checklist:
- Reconcile inventory: Confirm serial numbers, configurations, drive locations, and accessories against the CMDB.
- Capture evidence: Apply serialized labels and photograph rack positions, condition, and identifying marks.
- De-install safely: Power down systems, label cables, preserve rails and drive bays, and separate spinning drives, NVMe media, and self-encrypting drives.
- Pack to protect value: Use ESD protection, anti-static bags, foam blocking, and suitable palletization. Add shock indicators when the handling risk warrants them.
- Close the receipt loop: Match the receiving report to the pickup manifest, then connect each serial to its sanitization or destruction certificate and settlement record.
Choose freight by equipment risk and handling needs. White-glove service fits dense data center pulls and sensitive systems. Blanket-wrap transport reduces repacking for larger equipment. LTL suits properly palletized, lower-risk loads, while secure transport is appropriate for high-risk media before sanitization.
Use tamper-evident seals, two-person handoff logs, and GPS-tracked vehicles when data classification or contract terms require them. The IT asset disposal chain-of-custody framework connects physical movement with the final audit file. That file should reconcile custody, serials, data treatment, disposition, and payment.
Pricing for Maximum Recovery in an AI-Driven Secondary Market
Book value is an accounting position, not a market price. The secondary market now responds to workload fit, component scarcity, configuration, and AI infrastructure demand. A server with high memory capacity, usable GPU support, or scarce replacement parts may attract stronger interest than a newer but oversupplied configuration.
The broader ITAD market was valued at USD 7.74 billion in 2025, projected at USD 8.67 billion in 2026, and projected to reach USD 21.51 billion by 2034, implying a 12.3% compound annual growth rate, according to this 2026 ITAD market report. The same benchmark lists an illustrative 2026 Q1 resale value of USD 404 per enterprise server, up 95.6% year over year, with AI/GPU servers at USD 20,287 per unit and laptops at USD 170 per unit.
Price by demand band
Use separate bands for current-generation, still-supported, aging-but-functional, and parts-only equipment. Grade Dell PowerEdge, HPE ProLiant, and Cisco UCS systems by processor generation, memory population, storage, networking, GPU compatibility, and remaining support relevance. Specific NVIDIA cards should be valued by model, memory, form factor, tested condition, and the server platform that houses them.
Independent reporting found server resale values in 2025 reached roughly 2.5 times their seven-year average, with some facilities reporting jumps of 328% and 417%. Laptop averages also rose from $93.50 to $125.31 year over year, as reported by Resource Recycling.
Set a floor price from current comparable sales, testing cost, logistics, and expected recovery. Use a reserve floor for auctions, and establish a market-trigger rule that forces revaluation when demand, component availability, or the next refresh cycle changes. Sell quickly when a high-demand configuration is still scarce. Choose graded remarketing when testing and slower channel development can justify the added recovery.
Contracts, Transfer of Liability, and Post-Sale Reporting
The bill of sale doesn't close the risk. Your ITAD agreement should define exactly what happens to each asset from pickup through final resale, recycling, destruction, or export.
Clauses procurement should insist on
- Defined scope: Identify locations, asset classes, services, exclusions, and project milestones.
- Sanitization standard: Reference NIST SP 800-88 Rev. 1 and specify when clear, purge, or destroy applies.
- Liability language: State when custody and ownership transfer, and identify responsibility for loss, unauthorized access, environmental violations, and export issues.
- Certification requirements: Require serial-level certificates and a reconciliation process for missing or mismatched assets.
- Environmental controls: Require accountable downstream processing and applicable R2v3 or e-Stewards responsibility.
- Commercial settlement: Define valuation methodology, deductions, payment timing, returns, and treatment of non-working units.
Auditors reviewing SOC 2, HIPAA, or PCI evidence generally need traceable records that connect policy to individual assets. Insurance carriers may also ask how the organization controlled custody, verified destruction, and documented the provider's qualifications after an incident.
Close the loop with a usable report
The final package should include certificates of destruction, certificates of sanitization, remarketing proceeds statements, recycling documentation, diversion information for ESG reporting, the signed bill of sale, and a retention schedule. Keep the report readable enough for finance and detailed enough for security. A spreadsheet without certificates, custody events, and serial reconciliation isn't an audit file.
Beyond Surplus offers business IT equipment buyback, secure data wiping and hard drive shredding, electronics recycling, product destruction, data center de-installation, logistics coordination, and certificates supporting disposition records.
Contact Beyond Surplus to evaluate your enterprise laptops, servers, networking equipment, and data center assets for secure sanitization, documented chain of custody, and value recovery. Share your inventory and retirement timeline so the disposition plan can match market timing, compliance requirements, and the evidence your auditors will request.


